Starting February 15, 2026, code signing certificate lifespans are limited to a maximum of one year. As a result, DigiCert now offers only 1-year code-signing certificate plans.
Good News:
With Certera & Sectigo Code Signing Certificates, you can still purchase multi-year terms using the “Install on Existing HSM” option to lock in the best per-year price and re-issue approximately after 400–460 days during the subscription period to ensure uninterrupted validity.
Key Takeaways A valid digital signature is a green light for Windows, browsers, and “Microsoft SmartScreen” protection: this file comes from the publisher mentioned in…
The shift from the FIPS 140-2 standard is significant for organizations making use of HSMs, software-based cryptographic modules, VPN equipment, secure communications, and other items…
Companies rush to utilise the potential of large language models; however, every new use case of generative AI introduces attack vectors previously unknown in traditional…
Quick Summary Globally, companies are still preparing for a quantum revolution, and the National Institute of Standards and Technology (NIST) has made significant progress on…
With quantum computing soon changing the way things work in general, one of the areas that cybersecurity experts are most worried about is how digital…
Something big just happened in the cybersecurity world. And if you’re using OpenAI’s macOS apps… this affects you directly. OpenAI has rotated its macOS code-signing…
OWASP (Open Web Application Security Project) is a non-profit organisation that has been in existence since 2001. Its mission is to educate (provide direction) webmasters…
What is a TPM? A Trusted Platform Module (TPM) is a microcontroller designed to increase the levels of protection for computers, smartphones, and other devices…
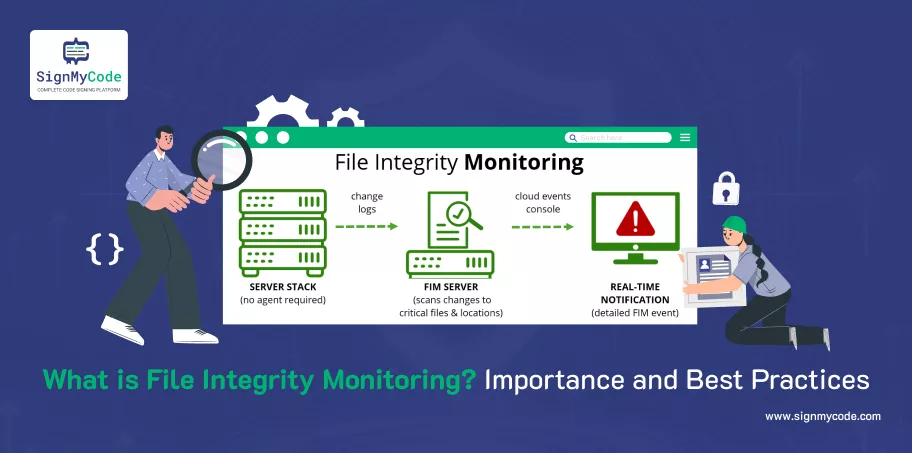
What is File Integrity Monitoring? File Integrity Monitoring (FIM) is a process that provides security by monitoring and verifying changes made to critical files, directories,…