Starting February 15, 2026, code signing certificate lifespans are limited to a maximum of one year. As a result, DigiCert now offers only 1-year code-signing certificate plans.
Good News:
With Certera & Sectigo Code Signing Certificates, you can still purchase multi-year terms using the “Install on Existing HSM” option to lock in the best per-year price and re-issue approximately after 400–460 days during the subscription period to ensure uninterrupted validity.
Published: December 23, 2025
The continuous changes in software development bring with them the necessity for the DCAS model – an amalgamation of development and operations processes – to…
Published: November 20, 2025
Microsoft Just Raised the Bar for Windows Drivers If you follow Windows development even casually, you already know this fact that drivers are the silent…
Published: November 7, 2025
What is a TPM? A Trusted Platform Module (TPM) is a microcontroller designed to increase the levels of protection for computers, smartphones, and other devices…
Published: November 6, 2025
Software has become the foundation of numerous companies and institutions worldwide, which has made the protection of source code critical in today’s digital environment. Code…
Last Modified: November 4, 2025
When people talk about securing software, they typically refer to two distinct aspects. The code itself, or the servers it runs on. That makes sense.…
Last Modified: November 4, 2025
Your CI/CD pipeline may also be the rocket that propels your business, but it can also be the silent killer that will blow up all…
Published: October 7, 2025
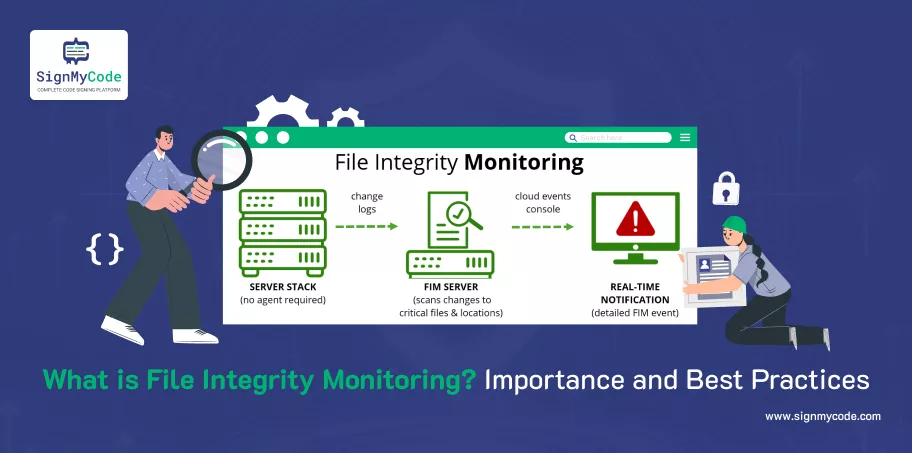
What is File Integrity Monitoring? File Integrity Monitoring (FIM) is a process that provides security by monitoring and verifying changes made to critical files, directories,…
Published: September 30, 2025
Digital certificates are designed to create trust. But what happens when hackers take advantage of gaps in trust? Reports show that Iranian state-sponsored hackers have…
Last Modified: September 24, 2025
Think of how painful it would be to spend a few weeks creating a mobile app to watch users abandon it because of a faulty…
Published: September 11, 2025
A New Supply Chain Attack in the npm Ecosystem On September 8, 2025, a large-scale npm supply chain attack quickly compromised 18 popular packages (with…
FREE GUIDE
Code Signing Best Practices for Developers
Secure your Software Signing Process and Prevent Software Compromises and Supply Chain Attacks.